Simplify CRA compliance with Torizon

Long-term embedded Linux maintenance, expert vulnerability analysis and secure OTA updates, so your team can focus on your product.

EU CRA Timeline
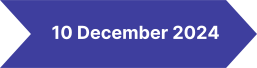
CRA entered into force

In Force
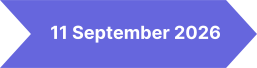
Reporting obligations are now in effect

Actively exploited vulnerabilities and severe security incidents trigger reporting obligations
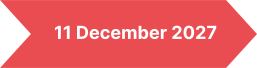
Full requirements go live!
Protect EU market access

Put product security, vulnerability handling and regular security updates in place


One Platform. Full Product Lifecycle.

Plan for at least 5 years of security support

Support must reflect your product's expected use: longer where needed, shorter only when expected use is shorter.

Security for your full product lifecycle

Plan for security from development through the support period. Build security in, then maintain and update devices as your product evolves.

Develop

Build security into your product

Develop your application while easily configuring the hardware security features and safeguards it needs.

Deploy

Document, validate and deliver securely

Connect OS evidence and validated releases in a repeatable, resilient deployment process.

Maintain

Handle vulnerabilities throughout the support period

Use OS vulnerability assessments, maintained releases and secure update delivery to support your team's response.

Dimitri Philippe
Dimitri Philippe

CEO, BE.services

I'm not saying go for Torizon and then everything is done. Being compliant is a manufacturer responsibility; it's about processes and using the right tools. But on top of all the functionality Torizon already provides, it helps you enormously with CRA compliance.


How Torizon Supports Your CRA Journey

CRA Requirements

How Torizon Helps

CRA requirement

Deliver security fixes

How Torizon helps

Secure updates

Update the OS and applications separately or together through one platform.

  • Remote and offline delivery

    Deliver updates securely, whether devices are online or offline.

  • Rollback and recovery mechanisms

    Automatically recover from failed updates to keep devices secure and operational.

  • Uptane-based update security

    Use a proven framework developed for the automotive industry to ensure trusted, tamper-resistant updates.

CRA requirement

Address vulnerabilities throughout the support period

How Torizon helps

Long-term OS maintenance

15+ years long-term support with proven history

  • Security and bug fixes for supported OS releases

  • Nightly builds continuously tested on real hardware

  • Guaranteed upgrade paths

  • Extended support available as a service

CRA requirement

Protect software integrity and sensitive data

How Torizon helps

Easy to use built-in security

Tools and documentation so you can easily enable hardware's security features

  • Secure Boot and chain-of-trust protection on supported hardware

  • Block device encryption for stored data

  • OP-TEE support for trusted execution

  • Encryption-key management backed by CAAM, TPM or TEE

CRA requirement

Identify and document your software components

How Torizon helps

Ready-to-use OS SBOMs

Accurately identified components for vulnerability scanning and compliance tools

  • Published component inventories for Torizon OS builds

  • SPDX and actionable CycloneDX formats

  • Downloadable evidence for your software documentation

CRA requirement

Assess vulnerabilities and decide what needs fixing

How Torizon helps

Expert vulnerability analysis

CVEs analyzed against a detailed/documented real-world product threat model

  • Continuous monitoring of published Torizon OS builds

  • Expert assessment of high and critical CVEs

  • Explained verdicts on vulnerability relevance

  • Analysis available as structured VEX documents ready to integrate in compliance reports and other tooling

The essence of what the CRA demands of you is to realistically assess the security risks your product is exposed to and design it so that it's resilient to all of those threats.

Jon Oster
Jon Oster

Torizon Security - Principal Developer

From Compliance to Solutions

Get practical insights on EU Cyber Resilience Act compliance from security and industry experts at the Torizon CRA Summit 2026. Explore real-world guidance on risk assessment, incident response, vulnerability management, and building CRA-ready products.

Webinar
Making Cybersecurity Compliance Easier: Risk Analysis and Threat Modeling
May 29, 2026
Watch now
Embedded Threat Modeling: Overcoming CRA Cybersecurity Challenges
Webinar
Embedded Threat Modeling: Overcoming CRA Cybersecurity Challenges
May 06, 2026
Watch now
How to Build CRA-Compliant Edge Device
Webinar
How to Build CRA-Compliant Edge Device
February 10, 2026
Watch now
Streamlining CRA Compliance: End-to-End Vulnerability Management for Embedded Linux with Torizon
Webinar
Streamlining CRA Compliance: End-to-End Vulnerability Management
October 28, 2025
Watch now
Making Cybersecurity Compliance Easier: Risk Analysis and Threat Modeling
Webinar
Making Cybersecurity Compliance Easier: Risk Analysis and Threat Modeling
October 08, 2025
Watch now
Embedded Linux EU Cyber Resilience Readiness with STM32MP2
Webinar
Embedded Linux EU Cyber Resilience Readiness with STM32MP2
April 30, 2025
Watch now
Simplify Development and Cybersecurity Compliance with Texas Instruments' Family of MPUs
Webinar
Simplify Development and Cybersecurity Compliance with Texas Instruments
April 10, 2025
Watch now
The Cyber Resilience Act is here
Blog
The Cyber Resilience Act is here
December 10, 2024
Learn More
Get a head start on EU Cyber Resilience Act compliance with Embedded Linux
Webinar
Get a head start on EU Cyber Resilience Act compliance with Embedded Linux
November 20, 2024
Watch now
Are you really ready for the new EU Cyber Resilience Act
Webinar
Are you really ready for the new EU Cyber Resilience Act?
October 04, 2024
Watch now
Getting Ready for the EU Cyber Resilience Act with Security Hardening of U-Boot
Blog
Getting Ready for the EU Cyber Resilience Act with Security Hardening of U-Boot
August 22, 2024
Learn More

Learn from our Experts how Torizon can help you simplify
CRA Compliance.

Free CRA consultation with our team.

Frequently Asked Questions

The CRA generally covers hardware and software sold in the EU with a direct or indirect data connection. Sector-specific exclusions apply, including certain medical products. Torizon supports embedded Linux security work; your product's intended use and classification determine its obligations.

Reporting obligations apply from 11 September 2026. Main product-security and conformity requirements apply from 11 December 2027. Prepare your reporting process now and build your security, update and documentation workflows. Torizon provides OS maintenance, vulnerability evidence and update delivery to support that work. Learn more.

Torizon provides Secure Boot, encryption and trusted-execution capabilities on supported hardware. Use them within your risk-based design, alongside production hardening and application security. Configure and validate the safeguards your product needs, including protection of data in transit.

Torizon publishes Software Bills of Materials (SBOMs) for its OS builds in SPDX and CycloneDX formats. Use them as the OS inventory for your product documentation, then account for your applications and added components. This gives you a documented starting point for the full product inventory.

Vulnerability Manager monitors published Torizon OS builds. Experts assess high and critical Common Vulnerabilities and Exposures (CVEs) and provide verdicts, rationale and Vulnerability Exploitability eXchange (VEX) reports. Your team can use that analysis to prioritize product-level investigation and remediation.

Manufacturers must report actively exploited vulnerabilities and severe security incidents: an early warning within 24 hours of awareness and a notification within 72 hours. Torizon's vulnerability evidence can inform your response. Your organization remains responsible for deciding when reporting is required and submitting it.

The CRA requires automatic security updates enabled by default where applicable, with user controls. Product context matters, especially in industrial environments. Torizon provides secure update delivery and rollback mechanisms; your team defines and validates the update policy appropriate to its product.

Yes. Torizon supports secure offline updates through local media, as well as remote updates for connected devices. You can deliver validated OS and application fixes without requiring every device to maintain an internet connection - learn more.

CRA support must reflect expected use, normally at least five years unless that use is shorter. Security updates are generally free to users. Torizon provides maintenance for supported OS releases and an extended-support service. Plan release upgrades or agreed coverage around your product's support period. Learn more.

Torizon supplies OS component records, vulnerability assessments and security capabilities. These support your technical documentation and security work. Your team completes the product risk assessment, user instructions, support information, conformity assessment and EU declaration of conformity before affixing the CE marking. Learn more.
?Haben Sie eine Frage